

DevOps Engineer
Jatin is an AWS-certified SysOps Administrator Associate with extensive expertise in AWS cloud services and a broad spectrum of DevOps tools.

Find your cloud savings in under 5 minutes

Get a $100 reward on signup

Being aware of the client's actual IP address is important in cloud-native architectures today—logging, geolocation, security, personalization, compliance, and rate limiting. Yet, when you add AWS load balancers to the equation, proxying can hide the original client IP. But don't worry: AWS provides solid mechanisms throughout its Load Balancer services to allow you to maintain or capture client IP information efficiently.

If your ALB forwards to AWS Lambda functions, the header still works. A typical Python excerpt: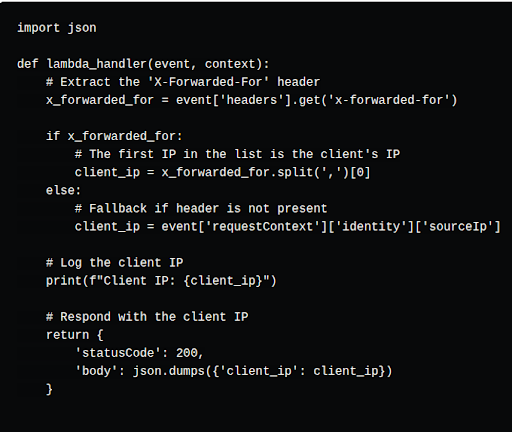
This pulls out the client's original IP (the first one in the list) and nicely falls through to the AWS Lambda's own sourceIp if the header is not present.
CLBs (Layer 4/7 hybrid) can support Proxy Protocol as an option:
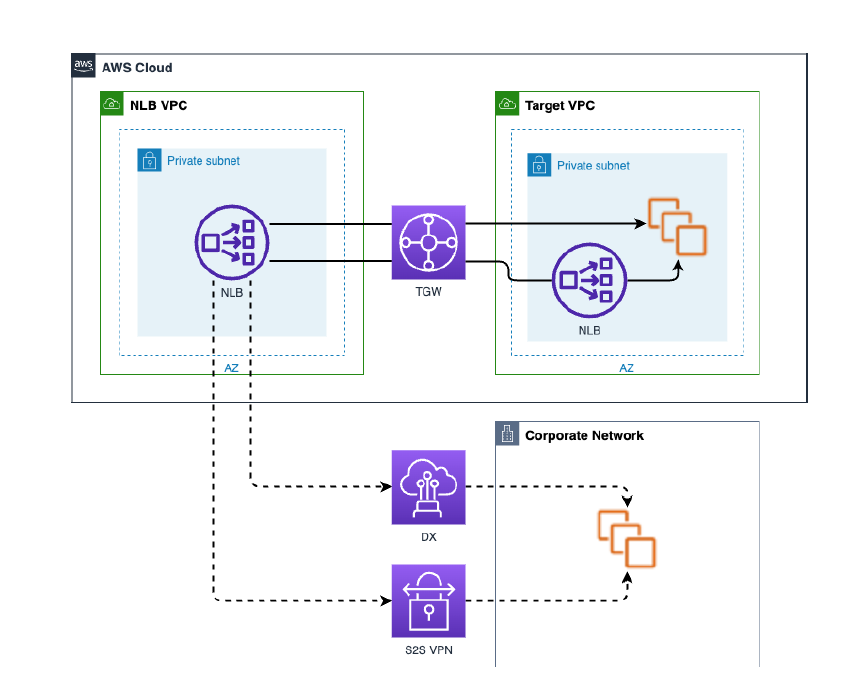
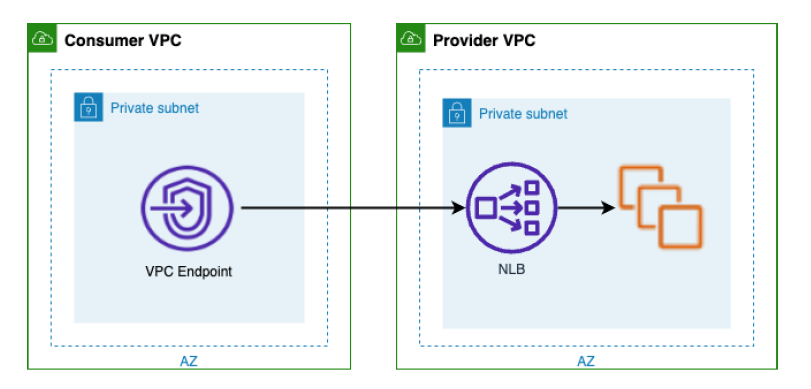
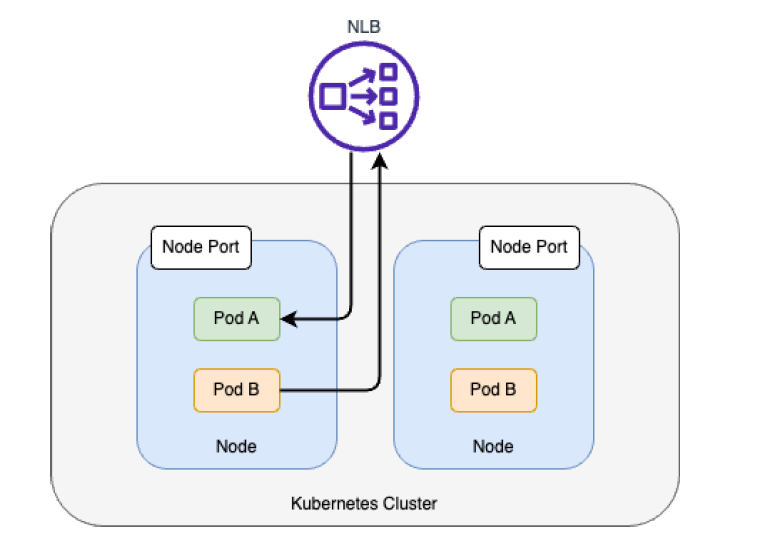
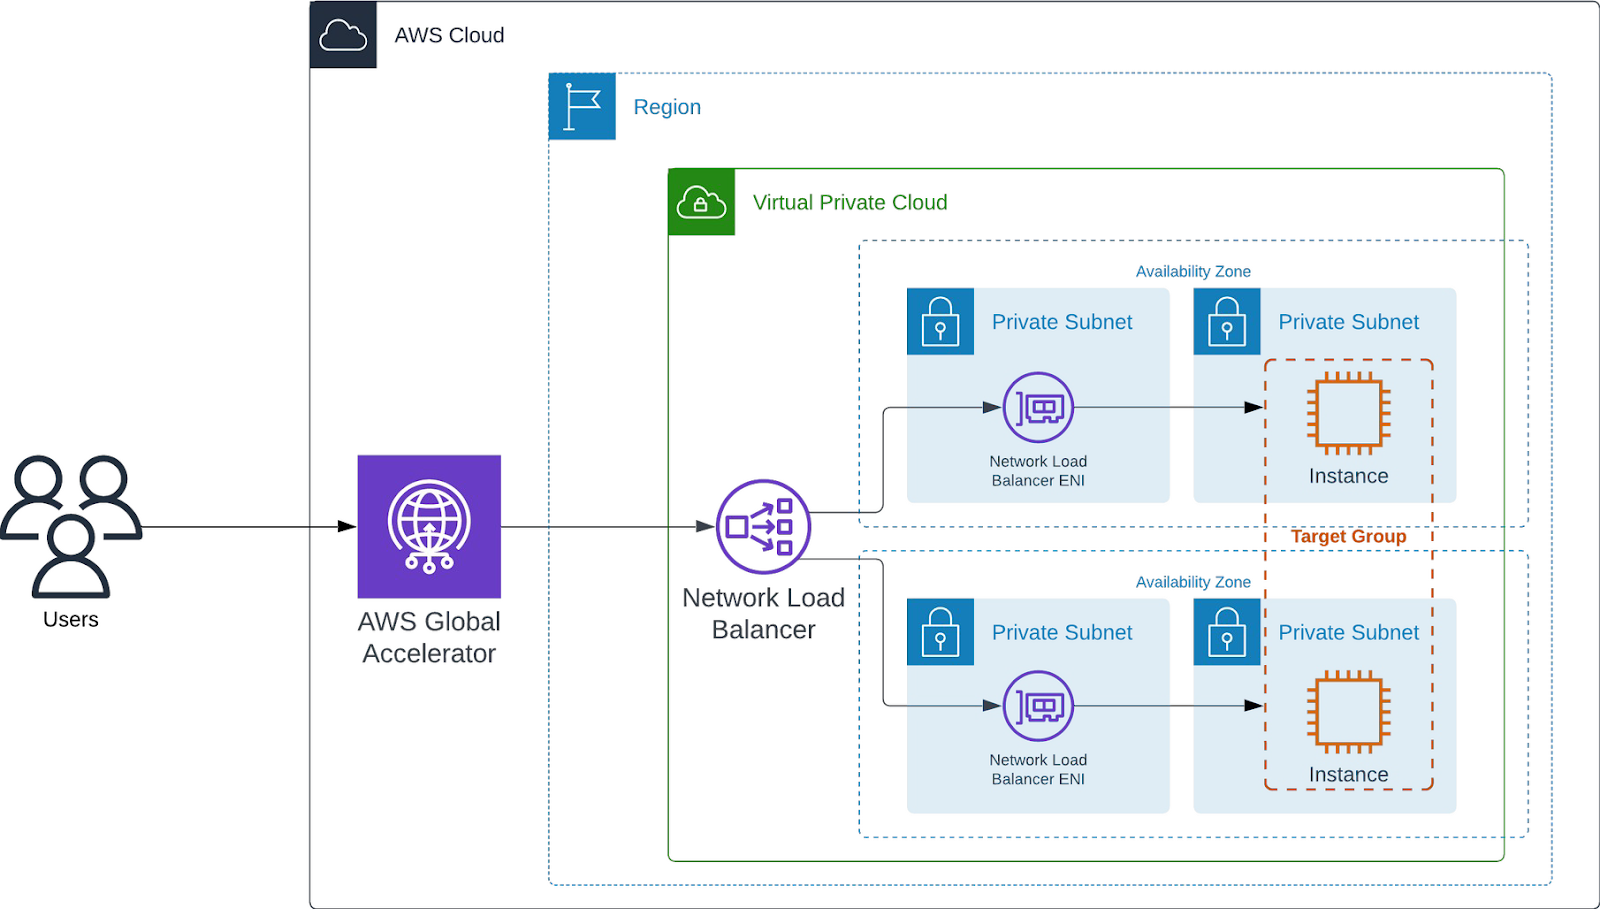
AWS Global Accelerator in front of an NLB makes client IP retention even more critical:
Both Accelerator and NLB should be set to keep the client IP.
| Service | Is Original Client IP Preserved? | How the Backend Gets the Client IP | Configuration | Key Considerations |
| Application Load Balancer (ALB) | Not as the backend connection's source IP | Through the X-Forwarded-For HTTP header | routing.http.xff_header_processing.mode controls whether ALB appends, preserves, or removes XFF | Layer 7 only. The backend TCP connection originates from the ALB, so applications must read XFF to identify the client |
| Network Load Balancer (NLB) | Yes, when client IP preservation is enabled or required by the protocol | Directly as the source IP in the IP packet | Controlled by the preserve_client_ip.enabled target group attribute for TCP/TLS | Behavior depends on target type and protocol. For some configurations, client IP preservation is enabled by default, while TCP/TLS IP target groups have it disabled by default |
| NLB with Proxy Protocol v2 | Client information is carried separately rather than relying only on the packet source IP | Through the Proxy Protocol v2 header | Enable proxy_protocol_v2.enabled on the target group | Useful when native source-IP preservation isn't available. The backend must understand Proxy Protocol v2 |
| AWS Global Accelerator + NLB | Yes, for supported NLB endpoints when client IP preservation is enabled | Original client IP reaches the NLB in the packet header and can continue to the backend | Enable client IP preservation on the supported Global Accelerator endpoint and configure the NLB appropriately | Requires an NLB with security groups. Client IP preservation isn't supported for NLB endpoints with TLS listeners |
AWS Global Accelerator + ALB
| Preserved to the ALB, then exposed to the backend through XFF | X-Forwarded-For at the application target | Global Accelerator client IP preservation plus ALB XFF processing | Global Accelerator can preserve the client source IP up to the ALB, but the ALB still terminates the connection and passes the IP to its targets through XFF |
The key difference is where the original client IP survives. With an NLB, supported configurations can preserve it at the network layer so the backend sees the client as the connection source. With an ALB, the backend sees a connection from the load balancer and retrieves the client's IP from X-Forwarded-For. Global Accelerator can preserve the original source IP as traffic enters AWS, but the endpoint behind it still determines the final behavior.
Capturing an actual client IP in AWS is load-balancer and architecture dependent:
Selecting the proper method provides greater logging, enhanced personalization, greater security, and regulatory compliance—all part of cloud computing applications today.
99% of companies saved up to 15% monthly with this plan & achieved peak performance.