
Find your cloud savings in under 5 minutes

Get a $100 reward on signup
Find your cloud savings in under 5 minutes
Get a $100 reward on signup

15+
Years of Cloud Excellence
1000+
Cloud Accounts secured
100+
Certified Cloud Security Specialists
Get a Free Security Assessment
CIS 1.14
Root account access keys still active
REMEDIATED
IAM.1
31 policies granting *:* on all resources
REMEDIATED
S3.8
Public block disabled on 6 buckets
REMEDIATED
KMS.3
Database credentials hardcoded in task definitions
REMEDIATED
SOC 2 CC7.2
No centralized threat detection across 14 accounts
IN FLIGHT
POSTURE ASSESSMENT · SAMPLE ACCOUNT
00 / 100
BEFORE
00 / 100
AFTER

Broad grants nobody's revisited since they were first written.
Public buckets, open ports, defaults that shipped straight to production.
Found by the auditor, not by you - the most expensive way to find out.
Hardcoded keys, no rotation, no vault, no owner.
A dozen dashboards, no single view of what actually matters.
Activity in progress with nobody watching the account.
Everything a security program needs, actually delivered - end to end by certified cloud security specialists.
DOMAIN 01 · BASELINE
DOMAIN 02 · COMPLIANCE
DOMAIN 03 · IDENTITY
DOMAIN 04 · SECRETS
DOMAIN 05 · DETECTION
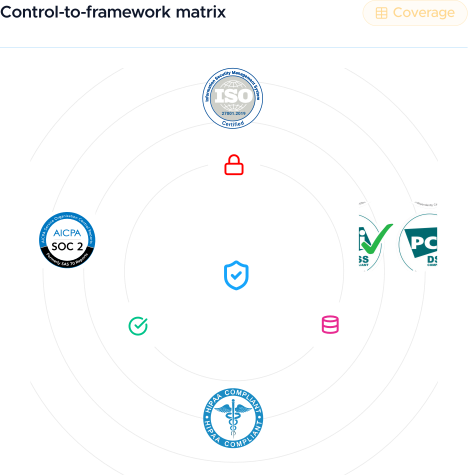
Logical access control, change management, continuous monitoring, incident response
PHI encryption, access audit trails, transmission security, workforce access limits
Network segmentation, cardholder data protection, key rotation, logging
Annex A technical controls with documented, repeatable evidence
Security Hub SOC 2 mappings · CloudTrail org trail · IAM Identity Center · GuardDuty
KMS + Config HIPAA pack · S3/EBS/RDS encryption rules · least-privilege roles
Config PCI pack · Secrets Manager rotation · VPC segmentation · WAF
Audit Manager assessments · conformance packs · exportable evidence
Proven expertise, practical security, and measurable outcomes that keep your cloud secure as you scale.
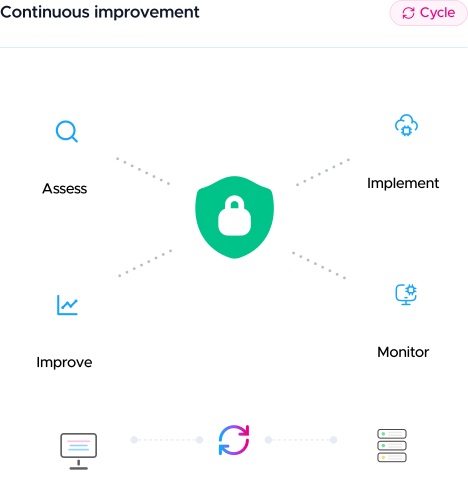
Engagement Process
A typical engagement runs six to ten weeks depending on account sprawl. It starts with a free assessment, and you keep the findings report either way.
Assess
Read-only role, automated scan across every account and region, and a manual review of your identity and network design. You get a ranked findings report with the blast radius of each issue spelled out in plain language.
Prioritise
We agree what gets fixed, what gets accepted as a documented risk, and who owns each item. Anything internet-facing or credential-related goes to the top.
Remediate
Our engineers implement the fixes alongside your team — hardening, IAM rebuild, secrets migration, encryption, detection rollout — in change windows you approve.
Automate
Config Rules, conformance packs and auto-remediation go live so the environment stays compliant after we leave. Drift becomes a ticket, not a finding at next year's audit.
Evidence
Continuous evidence collection, a monthly posture review, and an exportable pack your auditor can work from directly.
Major Player in MarketScape’s Worldwide FinOps Cloud Cost Optimization Assessment.
Major Player in FinOps Cost Management Products PEAK Matrix Assessment 2025.
Notable Vendor in Magic Quadrant for Public Cloud IT Transformation Services - Midmarket Global.
Product Challenger in APAC for AWS Ecosystem Partners 2025.
Frequently Asked Questions
A cloud security posture assessment reviews your cloud environment against a control baseline - usually CIS Benchmarks alongside your provider's own foundational security best practices (AWS FSBP, Azure Security Benchmark, or Google Cloud's security baseline) - and reports where your configuration deviates. CloudKeeper's assessment uses a read-only role, runs automated scans across all accounts, subscriptions or projects and regions, adds a manual review of your identity and network design, and delivers a ranked findings report within five working days. It is free and carries no commitment.
For a mid-sized AWS environment, the technical control work typically takes six to ten weeks: one to two weeks to assess and prioritise, four to six weeks to remediate, and two to three weeks to automate continuous evidence collection. Timelines stretch with the number of accounts, the amount of legacy IAM to unwind, and how much of your infrastructure sits outside infrastructure-as-code. Note this covers the technical controls only - policy documentation and the audit itself are handled by your auditor.
No. The assessment phase runs entirely on a read-only IAM role that you create and can revoke at any time. Write access is only requested for the remediation phase, is scoped to the specific changes agreed in the prioritisation step, and every change goes through a change window you approve. All actions are logged in your own CloudTrail.
Some controls do add cost - GuardDuty, Config, CloudTrail data events and extended log retention all carry charges. CloudKeeper models that cost before implementation and tunes it: right-sized log retention and lifecycle policies, selective data event logging, and regional scoping. Because we run FinOps engagements for the same customers, the security spend is presented alongside the savings rather than buried in next month's invoice.
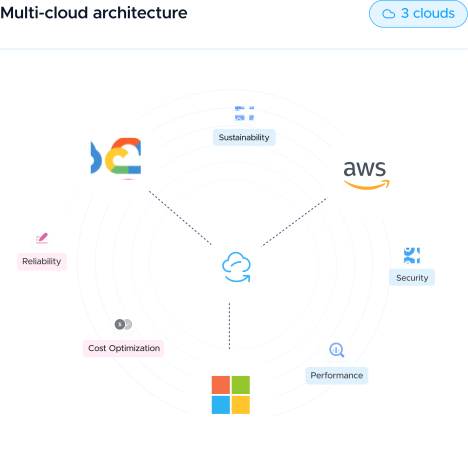
Yes - CloudKeeper supports multi-cloud environments across AWS, Azure, and GCP. Our engineering team includes certified cloud security specialists who handle baseline hardening, identity review, and compliance mapping natively on whichever cloud you run. Tell us your mix on the assessment call and we will scope accordingly.